 Yassine
Season 06 · Global
#632/ 7 797
Hack The Box Season 6 global ranking
Cybersecurity Engineer
Junior cybersecurity engineer passionate about ethical hacking and securing IT and industrial systems.
Key Strengths
Web, system, and network penetration testing (Linux & Windows), vulnerability exploitation, enumeration, and privilege escalation.
Digital evidence analysis, industrial controller investigations, intrusion detection, logging, and event correlation.
Design of secure multi-DMZ infrastructures, firewall, VPN, DNS, and LDAP configuration, and network monitoring.
Static/dynamic analysis, reverse engineering, secure cryptography design, and tooling scripts (Python, Bash, C, Java, PHP, Go, PowerShell).
Season 06 · Global
#632/ 7 797
Hack The Box Season 6 global ranking
2024 · France
#12in France
Hack The Box 2024 national ranking with 100+ rooted machines
01. Profile
Cybersecurity engineer trained at Grenoble INP ESISAR and ENSIAS, focused on offensive security, digital forensics and resilient infrastructure.
I combine applied research, penetration testing and hands-on CTF practice to turn complex technical findings into concrete remediation plans.
Hey there 👋 I'm Yassine, a cybersecurity engineer passionate about understanding and securing complex systems. I specialize in offensive security, vulnerability assessment and defensive hardening. I combine academic research with hands-on experience on Hack The Box and CTF competitions.
02. Skills
From attack simulation to forensic investigation and infrastructure hardening.
Web, system and network penetration testing, exploitation, enumeration and privilege escalation.
Digital evidence analysis, industrial controller investigations, intrusion detection and event correlation.
Secure multi-DMZ infrastructures, firewalls, VPN, DNS, LDAP and network monitoring.
Static and dynamic analysis, binary reverse engineering and protocol research.
Secure encryption methods and deep understanding of SSH, TLS and related protocols.
Python, Bash, C, Java, PHP, Go and PowerShell automation.
Hack The Box
Offensive skills measured in real conditions on the reference platforms.
YS4B
Hack The Box · Security profile
Breakdown of the documented reports by domain, target OS and difficulty.
picoCTF
158 challenges solved across exploitation, cryptography, reverse engineering and forensics.
03. Experience
Applied research, penetration testing and secure product development.
Forensic methods tailored to industrial PLCs.
Technologies: Wireshark, Binwalk, Python
Cybersecurity assessment of connected elevator infrastructure.
Technologies: Nmap, Metasploit, Burp Suite, SQLmap, Hydra, FFUF, Bash, Python

Web portal for internship management.
Technologies: PHP, HTML, CSS, MySQL, TCPDF
04. Projects
Security engineering projects spanning infrastructure, protocol research and software.
Designed a segmented architecture hosting identity, network and observability services.
Recreated CVE-2023-48795 against SSH and validated detection requirements.
Static and dynamic analysis of obfuscated Android malware.
Text embedding in JPEG images using DCT coefficient swapping.
Complete Active Directory domain with centralised identity and policy management.
Android application recommending the optimal access point.
05. Education
Double engineering degree
Computer Science, Networks & Cybersecurity
Engineering degree
Information Systems Security
Preparatory classes
MPSI / MP
06. Writeups
Structured reports covering exploitation, DFIR, SOC and malware-analysis challenges.
Scroll to spin the sphere, click a machine to open its report.
A structured Linux penetration-testing walkthrough covering enumeration, exploitation and privilege escalation.
Open writeup07. Achievements
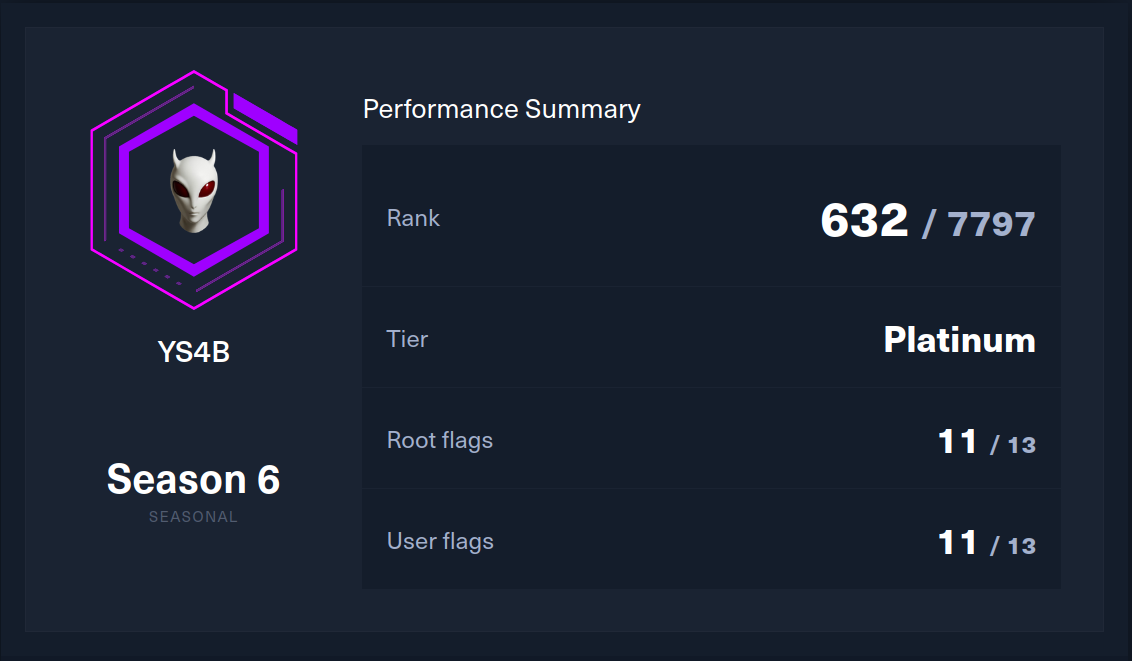
Platinum-tier season finish, ranked 632 out of 7,797.
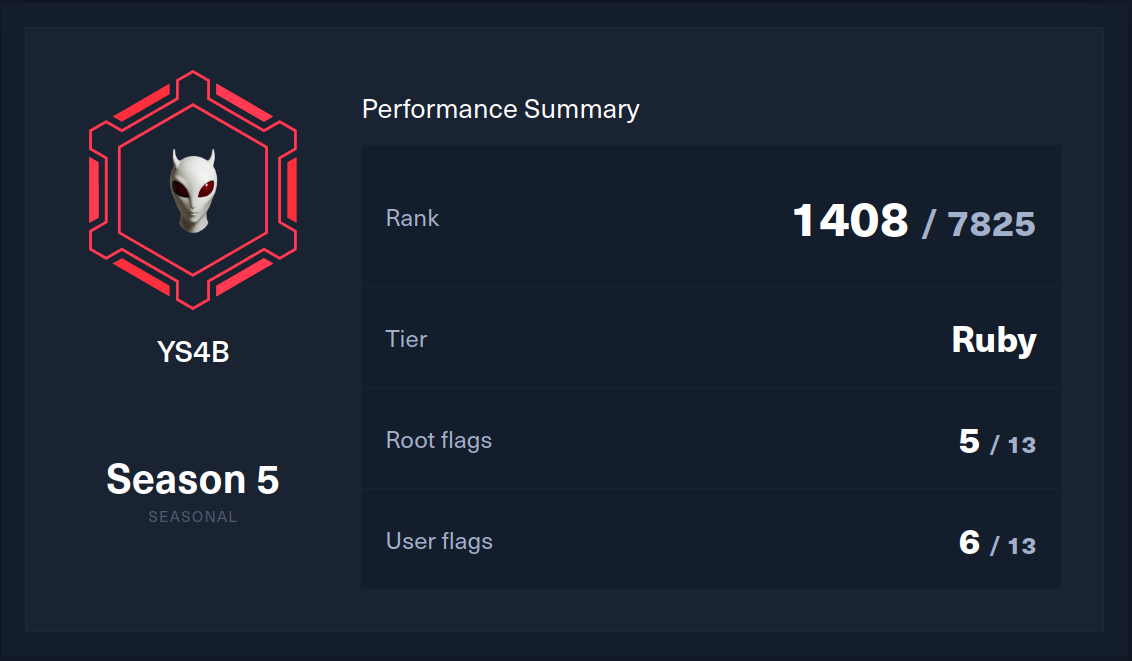
Ruby-tier season finish, ranked 1,408 out of 7,825.
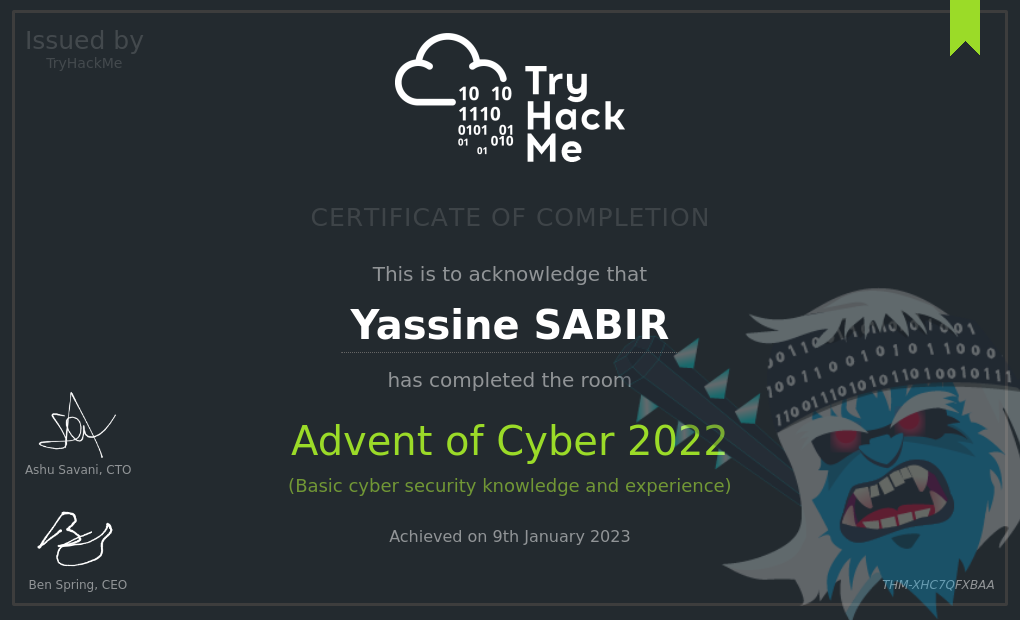
Completed the track covering exploitation and post-exploitation techniques.
Languages
Native fluency across personal and professional contexts.
Full professional proficiency with daily use in engineering programs.
Advanced level validated by TOEIC 850/990 and international teamwork.
Contact
Have a cybersecurity opportunity, research project or technical challenge? Let’s talk.
Private contact options
Write to sabir.yassine@proton.me. From another Proton Mail account the message is end-to-end encrypted automatically. From other providers it is only encrypted in transit (TLS) — use the OpenPGP option for end-to-end protection.
Email sabir.yassine@proton.meDownload my public key and encrypt your message locally with any OpenPGP client before sending it. Downloading the key does not encrypt anything by itself.
Checking public key…
For strong protection against key substitution, confirm this fingerprint through an independent channel (e.g. in person or on a profile you trust). HTTPS alone cannot prove the key is mine.